Resources
Tools and guides you can use to secure AI systems.
Coding Agent Security
Claude Code
The 28 settings and habits that recur in Claude Code incidents and research, each with its severity, the evidence behind it, and the fix.
A repeatable way to measure Claude Code exposure: a one-hour developer assessment, a six-phase team method, an enterprise checklist and a weighted maturity score.
A throwaway, offline, read-only container that audits your Claude Code setup in about a minute, with how-to-fix steps and OWASP, MITRE ATLAS and NIST AI RMF mapping.
Everything a developer should have in place before using Claude Code on company code, with a priority for each item and the audit check that verifies it.
Codex
The OpenAI Codex settings and habits behind documented CVEs and research, each with its severity, the evidence, and the fix.
A repeatable way to measure OpenAI Codex exposure: a one-hour developer assessment, a six-phase team method, an enterprise checklist and a weighted maturity score.
A throwaway, offline, read-only container that audits your OpenAI Codex config, rules, hooks and projects in about a minute, with how-to-fix steps and framework mapping.
Everything a developer should have in place before using OpenAI Codex on company code, with a priority for each item and the audit check that verifies it.
GitHub Copilot
The GitHub Copilot settings and habits behind documented CVEs and research, each with its severity, the evidence, and the fix.
A repeatable way to measure GitHub Copilot exposure: a one-hour developer assessment, a six-phase team method, an enterprise checklist and a weighted maturity score.
A throwaway, offline, read-only container that audits your VS Code agent settings, Copilot CLI and projects in about a minute, with how-to-fix steps and framework mapping.
Everything a developer should have in place before using GitHub Copilot agents on company code, with a priority for each item and the audit check that verifies it.
Cursor
The Cursor settings and habits behind documented CVEs and research, each with its severity, the evidence, and the fix.
A repeatable way to measure Cursor exposure: a one-hour developer assessment, a six-phase team method, an enterprise checklist and a weighted maturity score.
A throwaway, offline, read-only container that audits your Cursor sandbox, allowlists, MCP servers, hooks, CLI and projects in about a minute, with how-to-fix steps and framework mapping.
Everything a developer should have in place before using the Cursor agent on company code, with a priority for each item and the audit check that verifies it.
Gemini Code Assist
The Gemini CLI and Code Assist settings and habits behind documented CVEs and research, each with its severity, the evidence, and the fix.
A repeatable way to measure Gemini CLI and Code Assist exposure: a one-hour developer assessment, a six-phase team method, an enterprise checklist and a weighted maturity score.
A throwaway, offline, read-only container that audits your Gemini CLI and Code Assist settings, policies, MCP servers, extensions and projects in about a minute, with how-to-fix steps and framework mapping.
Everything a developer should have in place before using Gemini CLI or Gemini Code Assist agent mode on company code, with a priority for each item and the audit check that verifies it.
Books
Upcoming books
Securing Models, Applications, and AI Systems Across the Lifecycle
An Enterprise Framework for Secure, Responsible, Resilient, and Mission-Aligned Artificial Intelligence
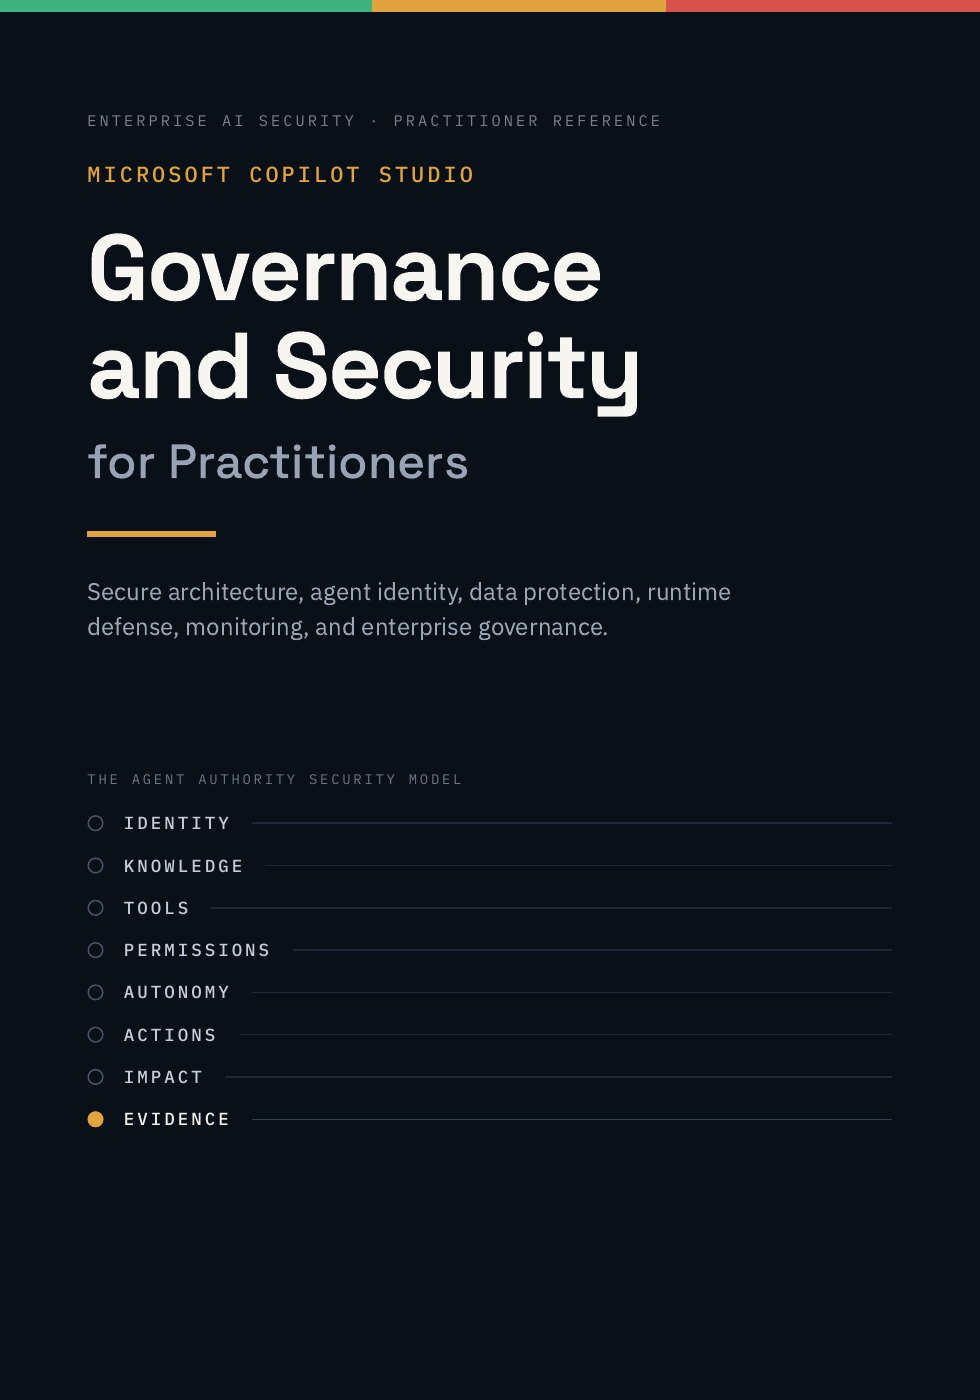
Secure Architecture, Agent Identity, Data Protection, Runtime Defense, Monitoring, and Enterprise Governance